Cyber News
AI-Generated Fake Login Pages Are Making Account Takeovers Easier
Identity Security / Artificial Intelligence
8 min read
Vulnerability / Mobile Security
Severity: CVSS 8.6 — Important
Affected product: Microsoft Authenticator for Android
Fixed version: 6.2606.4246 or later
Potential impact: Unauthorized access to email, files, calendars, and other Microsoft Graph resources, depending on the tokens obtained.
Reported exploitation status: Microsoft states that the vulnerability has not been exploited in attacks.
Recommended action: Update Microsoft Authenticator on Android devices and enforce a minimum application version through mobile device management where possible.
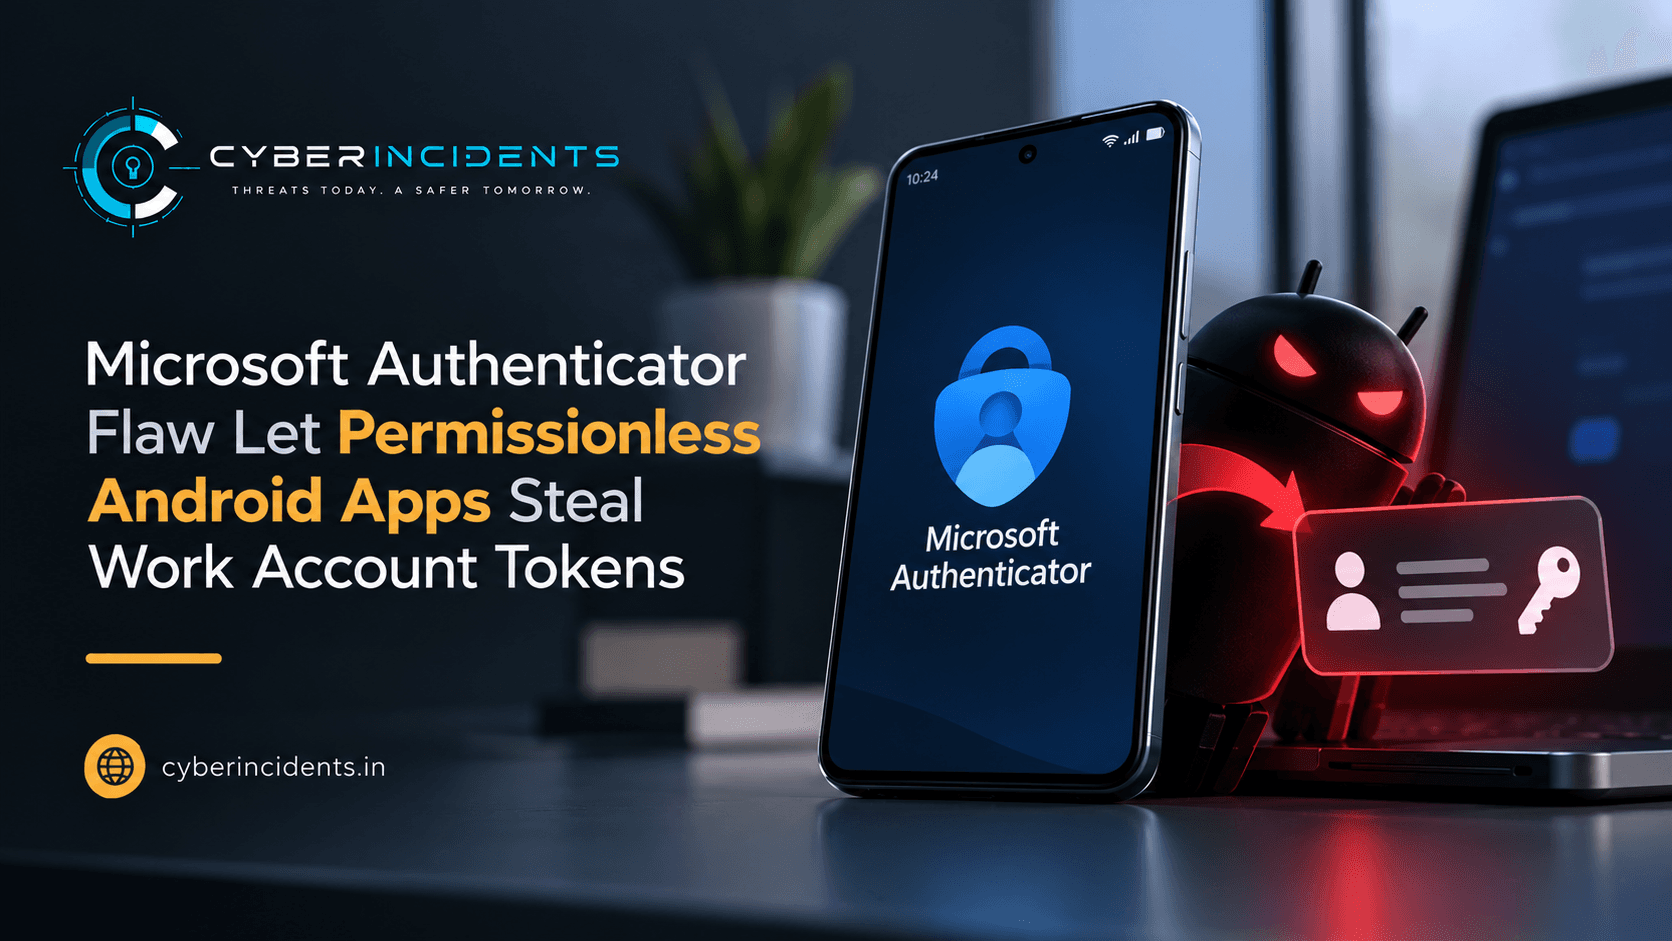
Microsoft fixed a security flaw in its Authenticator application for Android that could undermine the trust relationship between the authentication broker and applications requesting access to a user's Microsoft account.
The vulnerability, identified as CVE-2026-80097, was disclosed in technical research published by Ofek Levin through a fellowship program at Enclave on October 23, 2026. Microsoft assigned the CVE on September 8, 2026, and rated it 8.6 on the CVSS scale.
Microsoft Authenticator provides more than one-time verification codes. It also acts as an authentication broker for Microsoft applications such as Teams and Outlook. When a supported application needs to authenticate a user, it can request assistance from Authenticator, which supplies a token proving the user's authenticated identity.
Because these tokens can grant access to sensitive organizational resources, the broker must reliably verify which application is making the request.
According to Enclave's research, the vulnerability involved an exported Android activity named AccountChooserActivity. Any application on the device could start this activity and provide values used to construct an authentication request.
The attack relied on a failure to validate the requesting application's identity correctly.
The reported attack sequence was:
Malicious application installed: An attacker gets a malicious Android application installed on a device where Microsoft Authenticator contains a signed-in work account.
Authentication activity invoked: The application starts AccountChooserActivity and supplies parameters for a token request.
Trusted application impersonated: The malicious application claims to be a legitimate Microsoft application, such as Teams.
Signature validation bypassed: The signature check reportedly verifies the signature associated with the impersonated application rather than adequately validating the actual requesting application. If Teams is installed, its genuine signature is available, allowing the check to pass.
Authentication token obtained: Authenticator may return a token associated with the signed-in work account.
Potential resource access: The attacker could use an obtained token to access resources permitted by its associated scopes and permissions.
The central security weakness was the failure to bind token issuance to the identity of the application actually requesting the token.
In Enclave's proof-of-concept testing, tokens obtained through the vulnerability included Microsoft Graph permissions that could allow operations such as:
Reading and sending email.
Reading and modifying files.
Reading and modifying calendar information.
The actual impact depends on the token issued, its scopes, the user's privileges, and the resources accessible to the account.
A compromised work account could expose confidential business communications, documents, schedules, and other organizational information. Depending on the permissions available, an attacker could potentially use the account to send convincing internal messages or access additional business resources.
The issue concerns the work account signed into Authenticator on the affected device; the supplied report does not indicate that tokens for unrelated accounts are automatically exposed.
The research and Microsoft's advisory differ on the amount of user interaction required.
Enclave reported that its proof of concept could obtain tokens without user interaction beyond having a signed-in account present on the device. Microsoft, however, states that exploitation requires a malicious application to be installed and the victim to complete an authentication step in Authenticator.
This distinction matters when evaluating the attack's practicality. Organizations should use Microsoft's published advisory as the basis for official remediation requirements while treating the researcher's proof-of-concept findings as technical evidence of the potential impact.
Microsoft also states that the flaw was not exploited in attacks and was not publicly disclosed before the fix. As of October 26, 2026, it was not listed in the US CISA Known Exploited Vulnerabilities catalog.
Microsoft addressed CVE-2026-80097 in Microsoft Authenticator for Android version 6.2606.4246.
Recommended actions include:
Update Authenticator to version 6.2606.4246 or later.
Use Android enterprise mobility management to enforce a minimum application version where supported.
Verify compliance across corporate-owned and bring-your-own-device endpoints that access organizational resources.
Review identity and application sign-in telemetry for unusual access to Microsoft 365 resources.
If compromise is suspected, investigate affected sessions and tokens and follow the organization's identity incident-response procedures.
The supplied reporting does not establish whether installing the fixed version automatically invalidates tokens obtained before the update. Security teams should not assume that updating alone revokes previously issued tokens; assess session and token revocation requirements using Microsoft's guidance.
This vulnerability is primarily an application-level authentication flaw rather than a campaign associated with a specific attacker infrastructure. The supplied sources do not identify confirmed malicious IP addresses, domains, file hashes, or other campaign-specific indicators.
The following are useful investigation pivots, not standalone indicators of compromise:
| Indicator or pivot | Investigative relevance |
|---|---|
CVE-2026-80097 | Vulnerability identifier for reporting and asset-risk tracking |
AccountChooserActivity | Android activity associated with the reported attack path |
Microsoft Authenticator versions earlier than 6.2606.4246 | Potentially vulnerable application installations |
| Unexpected Microsoft Graph access | May warrant investigation when correlated with unusual sign-in or session activity |
Do not classify an endpoint as compromised solely because it has an older Authenticator version or because Microsoft Graph activity occurred. Correlate application version, device activity, identity logs, and evidence of unauthorized resource access.
Use Microsoft Intune or the organization's mobile device management platform to inventory devices running Microsoft Authenticator.
Identify installations below version 6.2606.4246.
Prioritize devices used to access sensitive Microsoft 365 accounts.
Check whether the affected devices comply with organizational application and device-security policies.
Confirm that remediation has reached devices that connect infrequently or are managed under bring-your-own-device policies.
Review Microsoft Entra ID sign-in logs and relevant Microsoft 365 audit data for unusual authentication or resource-access patterns.
Focus on:
Sign-ins from unfamiliar devices or unexpected locations.
Unusual access to Exchange Online, SharePoint, OneDrive, or calendar resources.
Unexpected increases in file downloads, mailbox access, or email-sending activity.
Access that differs from the user's established patterns.
Suspicious authentication activity shortly after a new or untrusted Android application was installed, if endpoint telemetry is available.
These behaviours are investigative leads, not proof that CVE-2026-80097 was exploited.
Where Android endpoint telemetry is available, correlate application installations and device events with identity-provider activity.
Look for evidence of an untrusted application installed on a device containing a signed-in work account, followed by anomalous Microsoft 365 access.
Because the reported flaw involves local Android application behaviour, cloud sign-in logs alone may not identify the specific exploitation mechanism. Preserve relevant device telemetry and escalate suspicious cases for deeper mobile application and identity investigation.
Track remediation through a compliance dashboard or vulnerability-management workflow. Confirm that the fixed version is installed, document exceptions, and follow up on devices that remain vulnerable.
Patch immediately: Ensure Microsoft Authenticator for Android is updated to version 6.2606.4246 or later.
Enforce application compliance: Apply minimum-version requirements to managed Android devices where supported.
Restrict untrusted applications: Use approved application sources and organizational mobile security controls.
Monitor identity activity: Alert on suspicious access to Microsoft 365 resources, particularly when combined with anomalous device or sign-in context.
Investigate suspected exposure: Review sessions, relevant audit logs, and affected resources. Revoke sessions or tokens when warranted under Microsoft's current incident-response guidance.
Validate remediation independently: Confirm the installed application version instead of relying only on update deployment status.
Educate users: Remind employees to install approved applications and report unexpected authentication prompts.
Continue reading
Cyber News
Identity Security / Artificial Intelligence
Cyber News
Category: Identity Security Secondary Categories: Email Security, Phishing, Cloud Security
Cyber News
Category: AI Security Secondary Categories: Supply Chain Attacks, Credential Theft, Prompt Injection
3 entries, most recent posts.
Homograph attacks
Identity Security / Artificial Intelligence
Agentic AI Security & Autonomous Attacks