The vulnerability is especially relevant in architectures involving reverse proxies, load balancers, web application firewalls (WAFs) and application servers.
Primary risk: Request desynchronisation between HTTP processing components.
Common targets: Reverse proxies, load balancers, CDNs and back-end web servers.
Potential impact: Access control bypass, request routing manipulation, cache poisoning and exposure of other users’ requests.
Key investigation evidence: HTTP headers, raw request data, proxy logs, back-end logs and connection timing.
Primary defences: Consistent HTTP parsing, strict request validation, secure proxy configuration and connection management.
1. When Two Servers Disagree
Imagine an organisation operates a web application behind a reverse proxy.
Every incoming request passes through the proxy before reaching the application server. The proxy inspects requests, applies security rules and forwards permitted traffic to the back end.
Both components are expected to agree on where one HTTP request ends and the next begins.
But what happens when they interpret the same request differently?
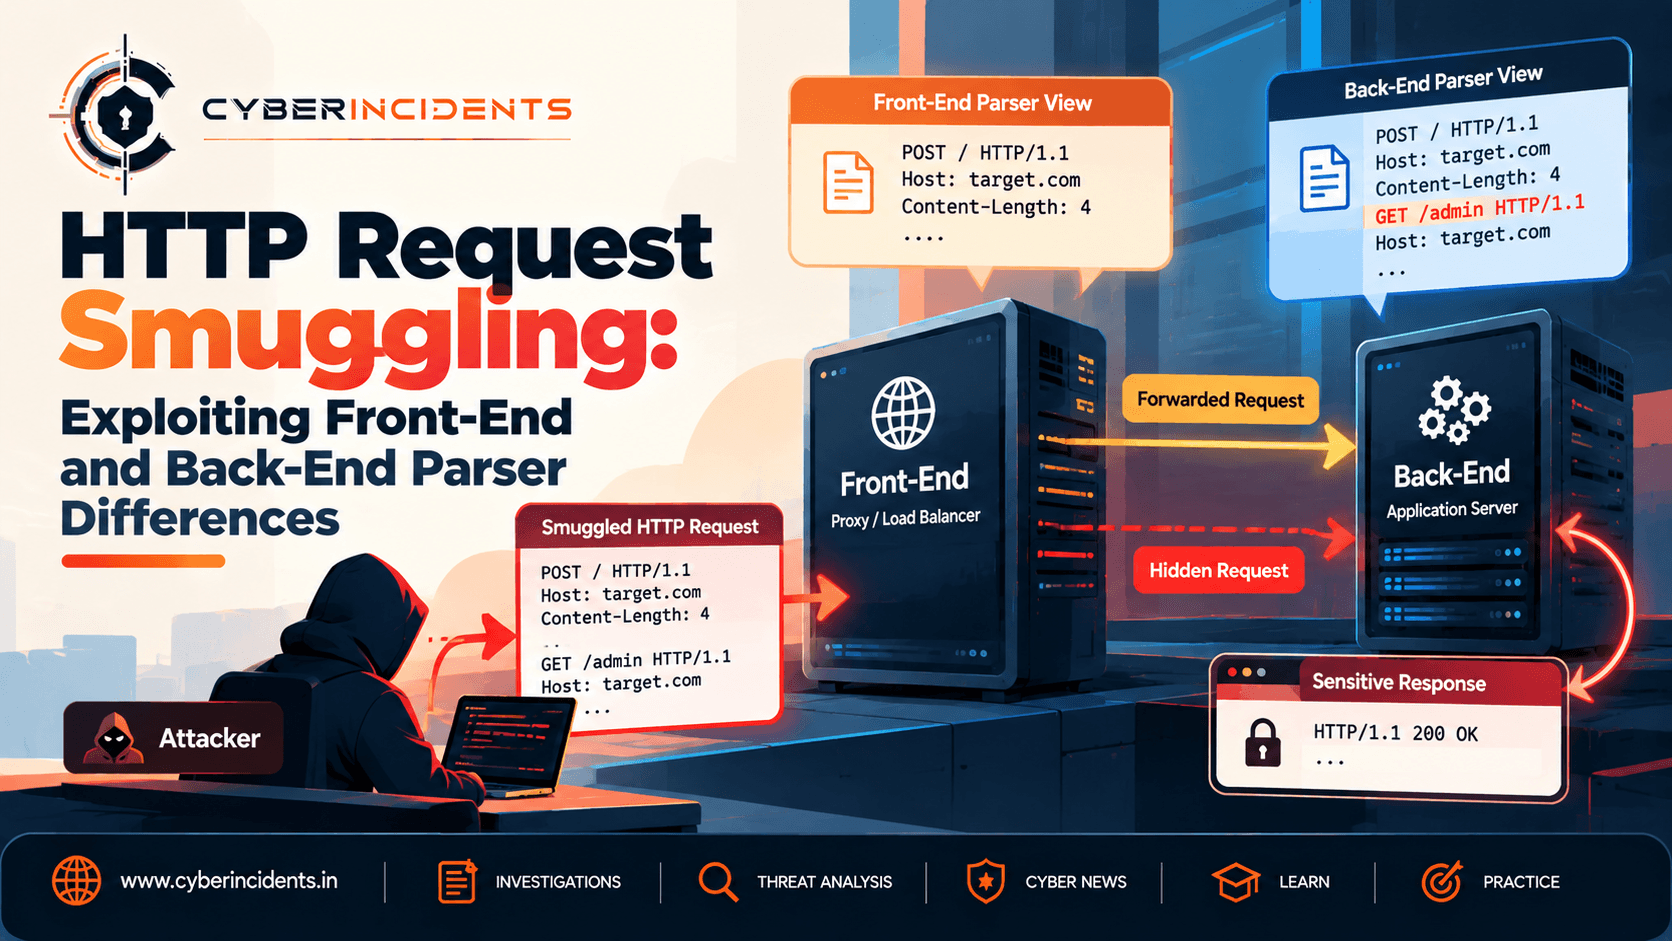
The front-end server might believe a request ends at one point, while the back-end server believes it ends somewhere else. This disagreement can cause the back end to process data as a separate request even though the front end considered it part of the original request.
This behaviour is known as HTTP request smuggling.
The central issue is not necessarily a failure to encrypt traffic or authenticate a user. It is a disagreement over the structure and boundaries of HTTP messages as they pass through multiple components.
2. Understanding the Architecture
HTTP request smuggling most commonly becomes relevant when HTTP traffic passes through multiple systems that parse or transform requests.
A typical architecture looks like this:
<box border radius="lg" padding={3} gap={2}>
<box background="surface-secondary" radius="md" padding={3} align="center" gap={1}>
<icon name="monitor" size="xl" />
**Client / Attacker**
<text size="sm" color="secondary">Sends an HTTP request</text>
</box>
<box align="center" gap={1}>
<icon name="arrow-down" size="lg" color="secondary" />
</box>
<box background="surface" border radius="md" padding={3} align="center" gap={1}>
<icon name="shield-check" size="xl" />
**Front-End Proxy / Load Balancer**
<text size="sm" color="secondary">Parses, filters and forwards requests</text>
</box>
<box align="center" gap={1}>
<icon name="arrow-down" size="lg" color="secondary" />
<text size="xs" color="secondary">Potential parsing disagreement</text>
<icon name="alert-triangle" size="lg" color="danger" />
</box>
<box background="surface" border radius="md" padding={3} align="center" gap={1}>
<icon name="server" size="xl" />
**Back-End Application Server**
<text size="sm" color="secondary">Interprets the forwarded HTTP message</text>
</box>
<text color="secondary" size="xs">Illustrative architecture: actual request handling depends on the proxy, protocol and server configuration.</text>
</box>
The front end may be responsible for internet-facing security controls, while the back end processes application logic. If their HTTP parsers disagree, those controls may not apply to the request the back end ultimately processes.
This is why request smuggling is particularly important in distributed web architectures.
3. How HTTP Determines Request Boundaries
HTTP/1.1 uses message framing rules to determine where request headers end, how a message body is represented and where the next request begins.
Two important headers are involved in many request-smuggling vulnerabilities.
Content-Length
The Content-Length header specifies the length of the message body in bytes.
A component that uses this header to frame a request expects the body to contain the specified number of bytes.
Transfer-Encoding
The Transfer-Encoding header can specify how a message body is transferred. In HTTP/1.1, Transfer-Encoding: chunked indicates that the body uses chunked framing, where chunks are preceded by their sizes and the message body ends with a terminating chunk.
Problems can arise when a front end and back end apply different framing rules to the same message.
For example, one component might rely on the declared content length, while another gives precedence to chunked transfer coding. The two components can consequently disagree about which bytes belong to the current request.
The important distinction is that these headers are not inherently malicious. They are legitimate HTTP mechanisms. The vulnerability arises when the systems processing them behave inconsistently or fail to reject ambiguous messages.
4. The Main Types of HTTP Request Smuggling
CL.TE: Content-Length versus Transfer-Encoding
In a CL.TE scenario, the front end uses Content-Length to determine the request boundary, while the back end uses Transfer-Encoding.
If the two components calculate different boundaries, the back end may interpret part of the data as the beginning of another request.
Security implication: The proxy and back end may disagree about what was actually submitted, potentially allowing unintended requests to reach the application.
TE.CL: Transfer-Encoding versus Content-Length
In a TE.CL scenario, the front end follows chunked transfer coding, while the back end uses Content-Length.
The front end and back end may again disagree about where the first message ends.
Security implication: Unprocessed bytes can remain on a connection and potentially be interpreted differently by the next component.
TE.TE: Transfer-Encoding interpretation differences
In a TE.TE scenario, both components support transfer encoding, but they handle the header differently. Differences in parsing, normalization or rejection of unusual header representations can cause inconsistent behaviour.
Security implication: An attacker may attempt to exploit parser inconsistencies to create request desynchronisation.
The labels CL.TE, TE.CL and TE.TE describe classic HTTP/1.1 framing scenarios. They should not be treated as a complete taxonomy of every modern request-smuggling vulnerability.
5. What Can an Attacker Achieve?
Request smuggling does not automatically provide administrative access or code execution. Its impact depends on the application's routing, authentication controls, connection reuse, caching and the specific parser disagreement.
Access control bypass
A front-end proxy or WAF may inspect one interpretation of a request while the back end processes another. This can create a gap between what the security layer approves and what the application receives.
Web cache poisoning
If a cache and the origin server disagree about request boundaries or response association, an attacker may be able to influence content stored or served by the cache.
Successful cache poisoning depends on the cache architecture, request handling and the exact vulnerability.
Web cache deception
In certain configurations, request desynchronisation may interact with cache rules in ways that cause sensitive responses to be handled unexpectedly. This outcome is implementation-dependent and should not be assumed for every smuggling vulnerability.
Session and request interference
On shared or reused back-end connections, desynchronisation may affect how subsequent requests are interpreted. In vulnerable circumstances, this can interfere with requests belonging to other users.
The feasibility and impact depend heavily on connection handling and the server architecture.
Request routing manipulation
If the back end interprets data differently from the front end, a request may reach an unexpected application endpoint or be processed outside the intended security assumptions.
6. Investigating HTTP Request Smuggling in a SOC
Consider a hypothetical alert: a WAF records an ordinary-looking HTTP request, but the back-end application reports a malformed request shortly afterward. Several users then experience unexpected responses from the same application.
The SOC team must determine whether the behaviour is caused by request smuggling, a configuration defect, a deployment issue or unrelated application errors.
Step 1: Identify the affected architecture
Document the request path:
CDN or edge proxy.
WAF.
Load balancer.
Reverse proxy.
Back-end web server.
Application framework.
Record the HTTP versions used on each connection. A client-facing HTTP/2 connection may be translated into HTTP/1.1 upstream, making protocol conversion an important investigation area.
Step 2: Examine raw HTTP evidence
Collect the available request data from the front end and back end.
Look for:
Conflicting or repeated message-framing headers.
Unusual Content-Length values.
Unexpected Transfer-Encoding representations.
Malformed chunked bodies.
Inconsistent request sizes across components.
Differences between the request recorded at the proxy and the one processed by the back end.
Do not conclude that a request is malicious merely because it contains both framing-related headers. Determine whether the combination is valid under the applicable protocol rules and how each component handled it.
Step 3: Correlate front-end and back-end logs
Compare timestamps, request identifiers, connection identifiers, byte counts and response status codes.
Investigate cases where:
The front end records one request but the back end records multiple requests.
The back end reports a malformed request that has no clear matching client request.
Response codes or body sizes differ unexpectedly between layers.
Anomalous behaviour affects multiple requests sharing a connection.
Log limitations matter: some proxies normalise requests before logging, and some application logs omit raw request bodies. The absence of suspicious text in a log does not prove the original request was unambiguous.
Step 4: Examine connection reuse
HTTP request smuggling can depend on how connections are reused between the front end and back end.
Determine whether unexpected requests or errors occurred on a persistent connection and whether the proxy reused that connection for subsequent traffic.
Review connection resets, timeouts, protocol errors and unusual sequences of requests and responses.
Step 5: Assess potential impact
Once a parsing inconsistency is suspected, determine whether it enabled unintended application behaviour.
Review:
Access to restricted endpoints.
Unusual authentication or authorisation outcomes.
Cache entries and cache-key behaviour.
Responses that may have been associated with the wrong request.
Evidence of cross-user request interference.
Changes to application data or administrative actions.
Treat impact as unconfirmed until supported by evidence. A framing discrepancy is a significant finding, but it does not by itself prove that another user's data was exposed.
Step 6: Contain and validate
Where exploitation is plausible, work with the application and infrastructure teams to reject ambiguous requests, correct the parser or proxy configuration, and safely reset affected connection pools if necessary.
Preserve logs and relevant configuration before making changes. Then validate the fix in an authorised test environment and monitor for recurring anomalies.
7. Evidence and Detection Opportunities
HTTP request smuggling rarely has one universal indicator of compromise. Detection depends on the telemetry available at each layer.
Evidence sourceInvestigation focusWAF logsFraming-header anomalies, rejected requests and unusual rule matchesReverse proxy logsRequest lengths, parsing errors, redirects and response mismatchesLoad balancer logsConnection reuse, resets, timeouts and backend selectionWeb server logsMalformed requests, unexpected request sequences and status-code anomaliesApplication logsUnexplained endpoint activity or unexpected authentication outcomesCDN and cache logsCache anomalies and unexpected response behaviourNetwork telemetryConnection timing, byte counts and repeated errorsDeployment/configuration recordsRecent changes to proxies, protocol handling or web-server versions
Potential detection patterns
A detection rule can correlate several signals rather than rely on a single header:
Identify requests rejected or flagged for ambiguous HTTP framing.
Correlate front-end parsing errors with back-end malformed-request events.
Identify unexplained differences in request counts or response sequences across layers.
Investigate clusters of anomalous responses on reused connections.
Compare anomalies with recent infrastructure deployments and configuration changes.
A single 400 Bad Request, connection reset or unusual header is not proof of request smuggling. These events can occur during routine client errors, health checks and software upgrades.
8. Detection Engineering and MITRE ATT&CK
A useful detection strategy should focus on the behaviour and objective observed rather than assign a technique solely because a request-smuggling pattern appears.
For example, if evidence demonstrates that an attacker exploited a vulnerability in an internet-facing application, MITRE ATT&CK T1190 – Exploit Public-Facing Application may be relevant.
If the investigation establishes that the vulnerability was used to access sensitive information, additional mapping should reflect the specific behaviour and outcome supported by the evidence.
Request smuggling itself is a web protocol exploitation technique and is not represented by one universally applicable ATT&CK technique. Avoid mapping cache poisoning, credential theft, access-control bypass or other outcomes unless the investigation confirms them.
9. Preventing HTTP Request Smuggling
Standardise request parsing
Use supported, patched versions of reverse proxies, load balancers and application servers. Ensure components interpret HTTP framing consistently.
Reject ambiguous messages
Configure front-end and back-end systems to reject malformed or ambiguous framing rather than attempting to recover differently from the same request.
Where possible, ensure that the front end parses and safely re-serialises requests before forwarding them.
Handle protocol conversion securely
Modern deployments may accept HTTP/2 or HTTP/3 from clients and forward HTTP/1.1 to back-end servers. Review protocol translation carefully because differences between protocol representations can introduce request-desynchronisation risks.
Do not assume that enabling HTTP/2 or HTTP/3 automatically eliminates request-smuggling vulnerabilities.
Control connection reuse
Review persistent connection and connection-pooling behaviour. Ensure that malformed requests cannot leave residual data that is later interpreted as another request.
Keep infrastructure patched
Track security advisories for the specific proxy, CDN, WAF, load balancer and application-server products in use. Apply updates and review vendor-recommended mitigations.
Test in an authorised environment
Use a controlled staging environment to validate request parsing and connection behaviour. Security testing should be coordinated with infrastructure owners, especially where shared connections or production caches could affect other users.
Improve observability
Capture sufficient request metadata and cross-layer identifiers to correlate front-end and back-end behaviour. Avoid indiscriminate logging of authentication tokens, cookies or other sensitive data.
10. Incident Response Checklist
When HTTP request smuggling is suspected:
Preserve evidence: Collect relevant WAF, proxy, load balancer, server and application logs.
Map the request path: Identify every component that parses, translates or forwards HTTP traffic.
Check framing behaviour: Determine whether components interpreted the same request boundaries consistently.
Assess exposure: Investigate possible access-control bypass, cache manipulation and request interference.
Contain safely: Apply vendor-recommended mitigations and reject ambiguous requests. Coordinate any connection-pool reset or traffic restriction.
Correct the root cause: Patch affected software or correct unsafe proxy and server configuration.
Validate the fix: Retest under controlled conditions and monitor for recurrence.
Document confidence: Separate confirmed exploitation, suspicious behaviour and unverified hypotheses.
Conclusion
HTTP Request Smuggling exploits a fundamental assumption in multi-layer web architectures: that every component agrees on where an HTTP request begins and ends.
When front-end and back-end parsers disagree, security controls may inspect a different request from the one ultimately processed by the application. Depending on the environment, this can create opportunities for access-control bypass, cache attacks or interference with other requests.
For SOC analysts and incident responders, the most important task is to correlate evidence across the entire request path. For defenders, the priority is consistent HTTP parsing, strict handling of ambiguous messages, secure protocol conversion, patched infrastructure and reliable cross-layer monitoring.
The key lesson: A request is only as safely handled as the components that interpret it.
Further Reading
PortSwigger Web Security Academy — HTTP Request Smuggling
OWASP — HTTP Request Smuggling guidance and testing resources
RFC 9112 — HTTP/1.1
RFC 9113 — HTTP/2
MITRE ATT&CK — T1190: Exploit Public-Facing Application