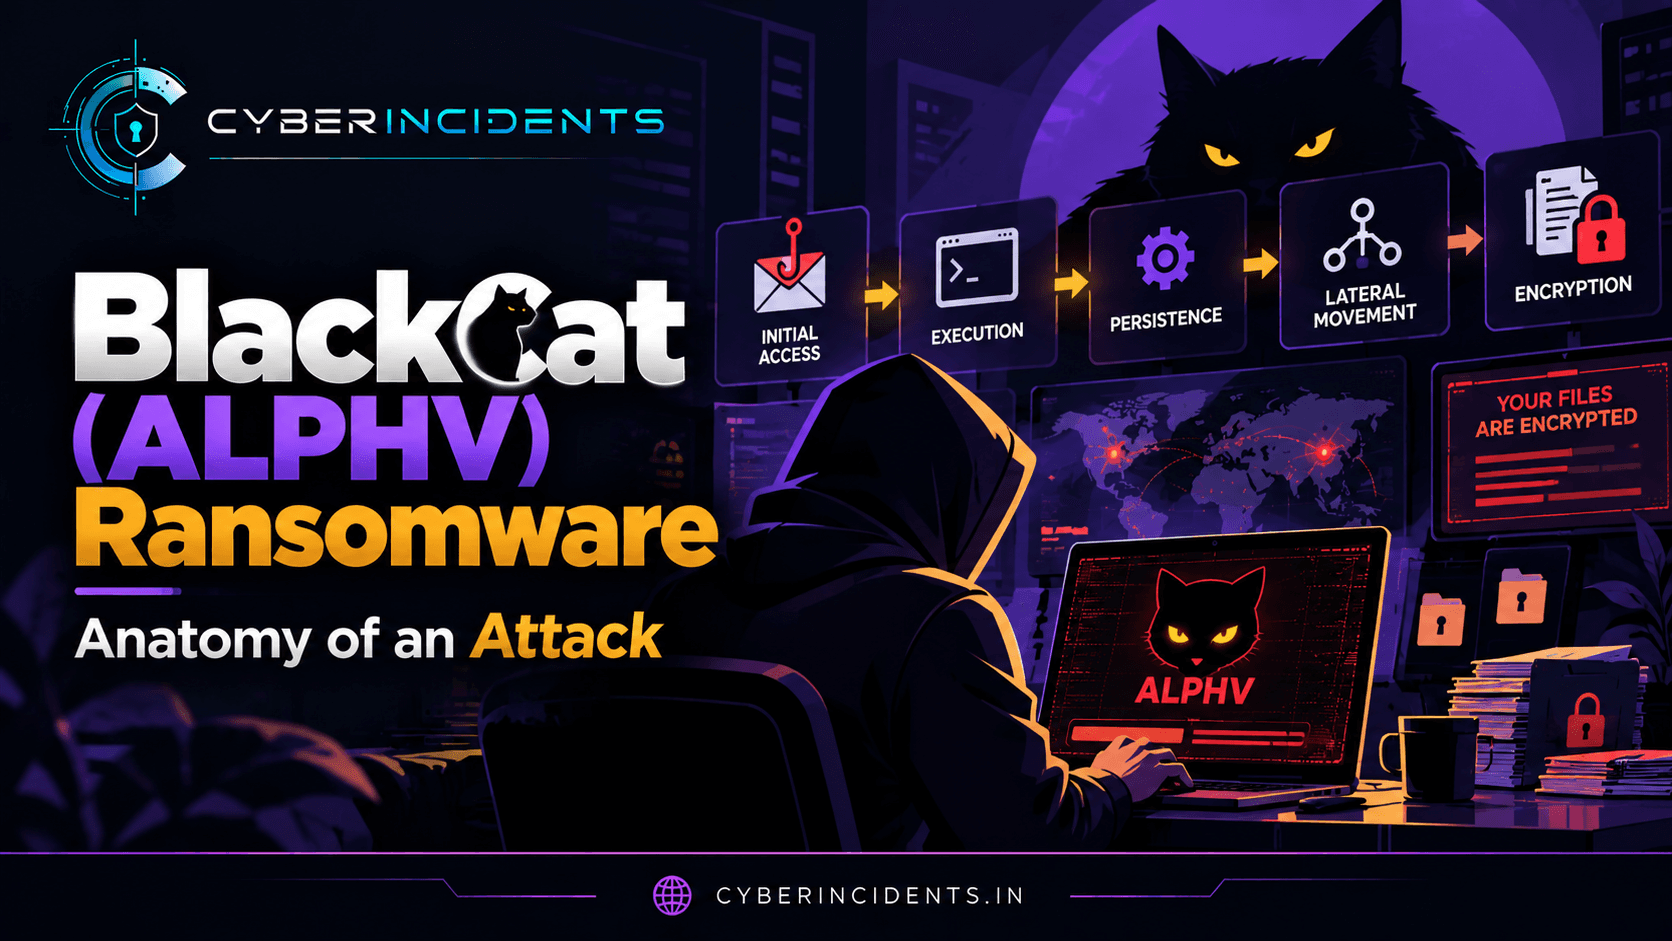
Introduction: Inside the BlackCat Ransomware Operation
Ransomware attacks rarely begin with encrypted files. In many incidents, the visible disruption is the final stage of an intrusion that may already involve compromised accounts, unauthorized access to servers, data theft, and attempts to weaken security controls.
BlackCat, also known as ALPHV, became notable for its ransomware-as-a-service (RaaS) model and its use of the Rust programming language. Under this model, the developers maintained the ransomware platform while affiliates carried out attacks against victims.
BlackCat was associated with double-extortion attacks, in which attackers stole sensitive information and then encrypted systems. This allowed them to threaten both operational disruption and the disclosure of stolen data.
The operation also became the subject of major law-enforcement action. In December 2023, the US Federal Bureau of Investigation announced that it had disrupted ALPHV/BlackCat infrastructure and developed a decryption tool that helped some victims recover data. The operation subsequently experienced further disruption, but historical reporting about the group should not be treated as proof that every related actor or copy of its tools disappeared.
For incident responders, BlackCat provides a useful case study in how ransomware operations combine technical intrusion methods with organized extortion.
What Made BlackCat Different?
BlackCat's use of Rust was a notable technical characteristic. Rust supports cross-platform development and provides memory-safety features, although using Rust does not automatically make malware harder to detect.
The ransomware platform also supported configurable behaviour. Depending on the version and deployment, operators could adapt aspects of the attack to the target environment.
Three characteristics were especially relevant to defenders:
Ransomware-as-a-service: Developers and affiliates could perform different roles within the operation.
Data theft and encryption: Some attacks combined the theft of sensitive information with disruption of systems.
Configurable deployment: Different affiliates and incidents could exhibit different behaviours, making a single detection rule insufficient.
This variability is important during incident response. Investigators should not assume that every BlackCat incident follows an identical sequence or produces the same indicators.
Stage 1: Initial Access
The first challenge for an attacker is gaining access to the target environment.
BlackCat affiliates used different initial-access methods across reported incidents. These included compromised credentials and exploitation of vulnerable systems. The exact method depended on the victim's environment and the affiliate conducting the operation.
Common entry points
Compromised credentials: Stolen usernames, passwords, or authentication material can provide access to remote services and internal systems.
Vulnerable internet-facing services: Unpatched or exposed services can create opportunities for unauthorized access.
Remote-access infrastructure: Poorly secured remote access can give an attacker a route into the organization.
Phishing and social engineering: Users may be manipulated into disclosing credentials or executing malicious content.
The presence of any one of these conditions does not establish a BlackCat infection. Attribution requires supporting evidence, such as observed ransomware behaviour, forensic artifacts, or reliable threat-intelligence reporting.
SOC investigation
Identify the earliest suspicious activity and reconstruct the events surrounding it.
Review identity-provider logs, VPN records, endpoint alerts, firewall data, and relevant application logs. Determine whether an unusual login was followed by unexpected process execution, privileged access, or connections to additional systems.
Establishing the initial entry point is essential because recovery is incomplete if the original access path remains open.
Stage 2: Execution and Establishing Access
After obtaining access, attackers need the ability to execute commands, run tools, or interact with compromised systems.
Depending on the intrusion, this may involve remote administration, malicious scripts, unauthorized software, or activity performed through an existing account.
Attackers may also establish persistence so they can regain access later. However, persistence mechanisms vary, and not every ransomware incident involves the installation of a persistent malware component.
SOC investigation
Examine endpoint process trees, command-line activity, suspicious services, scheduled tasks, and unexpected system changes.
On Windows systems, relevant telemetry may include:
Security Event ID 4688: Process creation, when process auditing is enabled.
System Event ID 7045: Service installation.
Security Event ID 4697: Service installation recorded by Security auditing, when configured.
Security Event ID 4720: User account creation.
Correlate these events with the account involved, the originating system, and the timing of other alerts. A single event is rarely enough to determine whether an intrusion is underway.
Stage 3: Credential Access and Privilege Escalation
Once inside an environment, attackers may attempt to obtain credentials or increase their privileges.
A compromised standard account may have limited access, while an administrator account could allow changes to servers, security controls, and recovery infrastructure.
Credential access and privilege escalation are related but distinct activities. An attacker may obtain another user's credentials without exploiting a local privilege-escalation vulnerability, or they may misuse an already privileged account.
Why this stage matters
The compromise of privileged credentials can transform a localized incident into a network-wide threat.
With sufficient access, an attacker may be able to administer additional systems, access sensitive data, or interfere with the tools an organization relies on to detect and contain attacks.
SOC investigation
Review authentication patterns, privilege assignments, account-group changes, and suspicious access to credential-sensitive resources.
Useful Windows Security events include:
4624: Successful logon.
4625: Failed logon.
4672: Special privileges assigned to a new logon.
4728: Member added to a security-enabled global group.
4732: Member added to a security-enabled local group.
These events must be interpreted in context. Compare the activity with the account's normal responsibilities, expected source systems, logon type, and surrounding endpoint activity.
Stage 4: Discovery and Lateral Movement
Attackers rarely stop at the first compromised endpoint if their objective is to disrupt a larger organization.
They may investigate the network to identify domain controllers, servers, shared folders, administrative accounts, and valuable data. If they obtain additional credentials or discover accessible systems, they may move laterally.
Legitimate administration tools can be abused during this stage, which means the presence of a familiar utility is not automatically evidence of malicious activity.
SOC investigation
Look for related activity across multiple systems rather than treating each alert separately.
Investigate:
Unexpected remote logons.
Accounts accessing servers they do not normally manage.
Unusual connections to file shares.
Suspicious remote process execution.
Administrative activity across multiple endpoints in a short period.
Access to backup infrastructure from unexpected hosts.
Correlate the events using timestamps, accounts, source endpoints, and destination systems. The objective is to reconstruct how far the attacker moved through the environment.
Stage 5: Defense Evasion and Security Control Tampering
Before ransomware deployment, attackers may attempt to reduce the effectiveness of security controls.
Potential activities include modifying endpoint protection settings, interfering with logging, stopping services, or changing configurations that could hinder detection.
Some ransomware operations also target backup and recovery mechanisms. If an attacker can weaken both production systems and recovery infrastructure, the organization may face a more difficult restoration process.
These behaviours are not exclusive to BlackCat, and legitimate administrators may perform similar operations. Investigators should assess whether the changes were authorized and consistent with normal maintenance.
SOC investigation
Prioritize unexplained changes to:
Endpoint protection and security services.
Audit and logging configurations.
Privileged accounts and access controls.
Backup policies and recovery services.
Administrative tools and system configurations.
An unexpected security-control change followed by suspicious remote access or activity across several servers should be treated as a potential escalation in the incident.
Stage 6: Data Theft and Double Extortion
One of the most significant risks in a BlackCat incident is that attackers may steal sensitive information before encrypting systems.
This approach is commonly called double extortion. The victim faces both the disruption caused by ransomware and the threat that stolen data will be published or disclosed.
The data may include customer information, business documents, financial records, intellectual property, or internal communications.
However, encryption does not prove that data theft occurred. Exfiltration must be investigated separately using network records, file-access telemetry, and other available evidence.
SOC investigation
Look for:
Unusual access to sensitive directories.
Unexpected data staging or compression.
Large or abnormal outbound transfers.
Connections to unfamiliar external destinations.
Access to cloud storage or file-transfer services outside normal patterns.
Correlate these events with the accounts and processes involved. Large transfers can have legitimate explanations, so destination, timing, process behaviour, and the type of data accessed all matter.
If data theft is suspected, preserve evidence and determine which data sets may have been accessed or transferred.
Stage 7: Backup Targeting and Recovery Inhibition
Backups are central to ransomware recovery. Attackers may therefore attempt to locate, modify, or delete recovery copies before deploying encryption.
Potential targets include backup-management servers, snapshots, recovery accounts, and storage systems holding protected data.
If backup infrastructure is accessible using the same compromised credentials as production systems, a single intrusion may threaten both the live environment and its recovery options.
SOC investigation
Review backup audit records for unexplained deletion, changes to retention policies, failed backup jobs, and unusual administrative access.
Correlate these events with privileged authentication and activity on other systems.
A suspicious backup deletion event can be an early warning of a ransomware operation, even when no files have yet been encrypted.
Stage 8: Ransomware Deployment and Encryption
Encryption is the most visible stage of a BlackCat attack, but it may occur after the attacker has already established extensive access.
The ransomware payload can make targeted files inaccessible, alter file names or extensions, and create ransom notes containing payment demands and instructions.
The exact execution pattern depends on the version and configuration. Not every incident produces identical file extensions or ransom-note names.
What defenders may observe
A sudden increase in file modifications.
Files becoming inaccessible.
Unexpected file extensions or ransom-note files.
Suspicious processes accessing large numbers of files.
Encryption activity across network shares or multiple endpoints.
Unusual activity involving servers and recovery infrastructure.
SOC investigation
Treat suspected mass encryption as an emergency.
Follow the incident-response plan to isolate affected systems and prevent further spread. Preserve endpoint and network evidence where feasible, identify the scope of affected systems, and investigate for signs of earlier credential compromise, lateral movement, and data theft.
Do not delay containment while waiting to identify the precise ransomware variant.
Incident Analysis: Connecting the Attack Chain
Consider a hypothetical BlackCat-related investigation.
An organization first identifies a suspicious remote login. Later, the same account accesses several internal servers, followed by unexpected administrative changes and unusual outbound data transfers. Shortly afterward, multiple endpoints begin generating alerts for mass file modification.
The first login alone may not establish a ransomware incident. The later events, however, suggest a possible progression from unauthorized access to lateral movement, data theft, and encryption.
A SOC team should correlate the evidence across identity, endpoint, network, and backup systems.
The investigation should answer five essential questions:
How did the attacker enter? Identify the initial access method and affected account or system.
What access did the attacker obtain? Determine whether credentials or privileges were compromised.
How far did the attacker move? Identify affected endpoints, servers, and shared resources.
Was data stolen? Examine evidence of staging and outbound transfer.
Can the attacker return? Verify that the original entry point and any remaining persistence have been addressed.
This approach helps investigators reconstruct the incident rather than focusing only on the final encrypted files.
Incident Response and Recovery
If BlackCat activity is suspected, organizations should coordinate the SOC, incident-response team, IT operations, and relevant business stakeholders.
1. Contain affected systems. Isolate compromised endpoints and servers where appropriate, and restrict suspicious access.
2. Secure identity infrastructure. Investigate compromised accounts, revoke sessions where necessary, and rotate exposed credentials from trusted systems.
3. Preserve evidence. Collect endpoint telemetry, authentication records, network logs, ransom notes, and relevant files according to forensic procedures.
4. Determine the scope. Identify affected systems, privileged accounts, shared storage, and backup infrastructure. Assess whether sensitive data may have been exfiltrated.
5. Protect recovery systems. Secure backups and verify that restoration copies remain available and trustworthy.
6. Eradicate the intrusion. Address the initial entry point, remove attacker access, and rebuild or clean systems as appropriate.
7. Restore and monitor. Recover systems from trusted sources and continue monitoring for renewed access, suspicious authentication, and unexpected system changes.
A ransom payment does not guarantee recovery or prevent the disclosure of stolen information. Recovery decisions should follow the organization's established incident-management, legal, and business-continuity processes.
Indicators of Compromise (IOCs) and Detection Notes
BlackCat has been associated with multiple versions and different affiliate operations. Indicators can vary between incidents and over time. A generic overview should not be treated as a complete, current IOC list.
The following are behavioural investigation leads, not confirmed BlackCat-specific IOCs.
Endpoint Indicators
Unexpected ransomware execution or mass file modification.
Suspicious processes accessing large numbers of files.
Unexpected changes to security services or logging settings.
Unexplained scheduled tasks, services, or account changes.
Ransom-note creation or sudden file-access failures.
Identity and Network Indicators
Unusual privileged logons.
Accounts accessing systems outside their normal responsibilities.
Unexpected remote sessions across multiple servers.
Abnormal outbound transfers or suspicious data-staging activity.
Unexpected changes to backup policies or recovery infrastructure.
Evidence to Preserve
For each relevant event, record:
Timestamp and affected hostname.
User account and logon type.
Process name, parent process, and command line where available.
Source and destination network details.
Relevant file paths and hashes.
EDR alert information and associated evidence.
Whether the behaviour is confirmed malicious, suspicious, or legitimate.
For a live incident, obtain version-specific indicators from trusted threat-intelligence sources and validate them against local telemetry. Do not label a file, domain, or IP address as a BlackCat indicator without supporting evidence.
Lessons for Security Teams
The BlackCat case highlights several defensive priorities:
Strengthen initial access controls: Patch exposed systems and protect remote access.
Secure privileged identities: Enforce strong authentication and limit standing administrative access.
Monitor lateral movement: Correlate endpoint, identity, and network events across the environment.
Protect security controls: Investigate unauthorized changes to logging and endpoint protection.
Keep backups isolated: Reduce the risk that compromised production credentials can also destroy recovery copies.
Investigate data theft: Assess possible exfiltration independently of encryption.
Prepare for rapid containment: Test response procedures before an incident occurs.
Conclusion
BlackCat (ALPHV) demonstrates how ransomware operations can combine unauthorized access, credential abuse, lateral movement, data theft, and encryption into a coordinated intrusion.
For SOC analysts, the most valuable evidence may appear long before a ransom note. Suspicious logins, unexpected privileged access, unusual outbound transfers, and backup tampering can reveal the attack while containment is still possible.
The central lesson is to investigate the full attack chain. Effective ransomware defence depends on understanding how access was obtained, what the attacker did inside the environment, whether data was stolen, and whether the attacker can return after recovery.