1. Introduction: The Website You Trust May Be the Beginning of an Attack
Imagine an employee visiting a familiar news website or a legitimate business portal. The page appears normal until a message suddenly claims that their browser requires an urgent update.
The notification looks convincing. It may imitate a familiar browser interface, use official-looking graphics, and display a prominent update button. The employee downloads the offered file and opens it, believing they are installing a legitimate update.
Instead, they have started a malware infection.
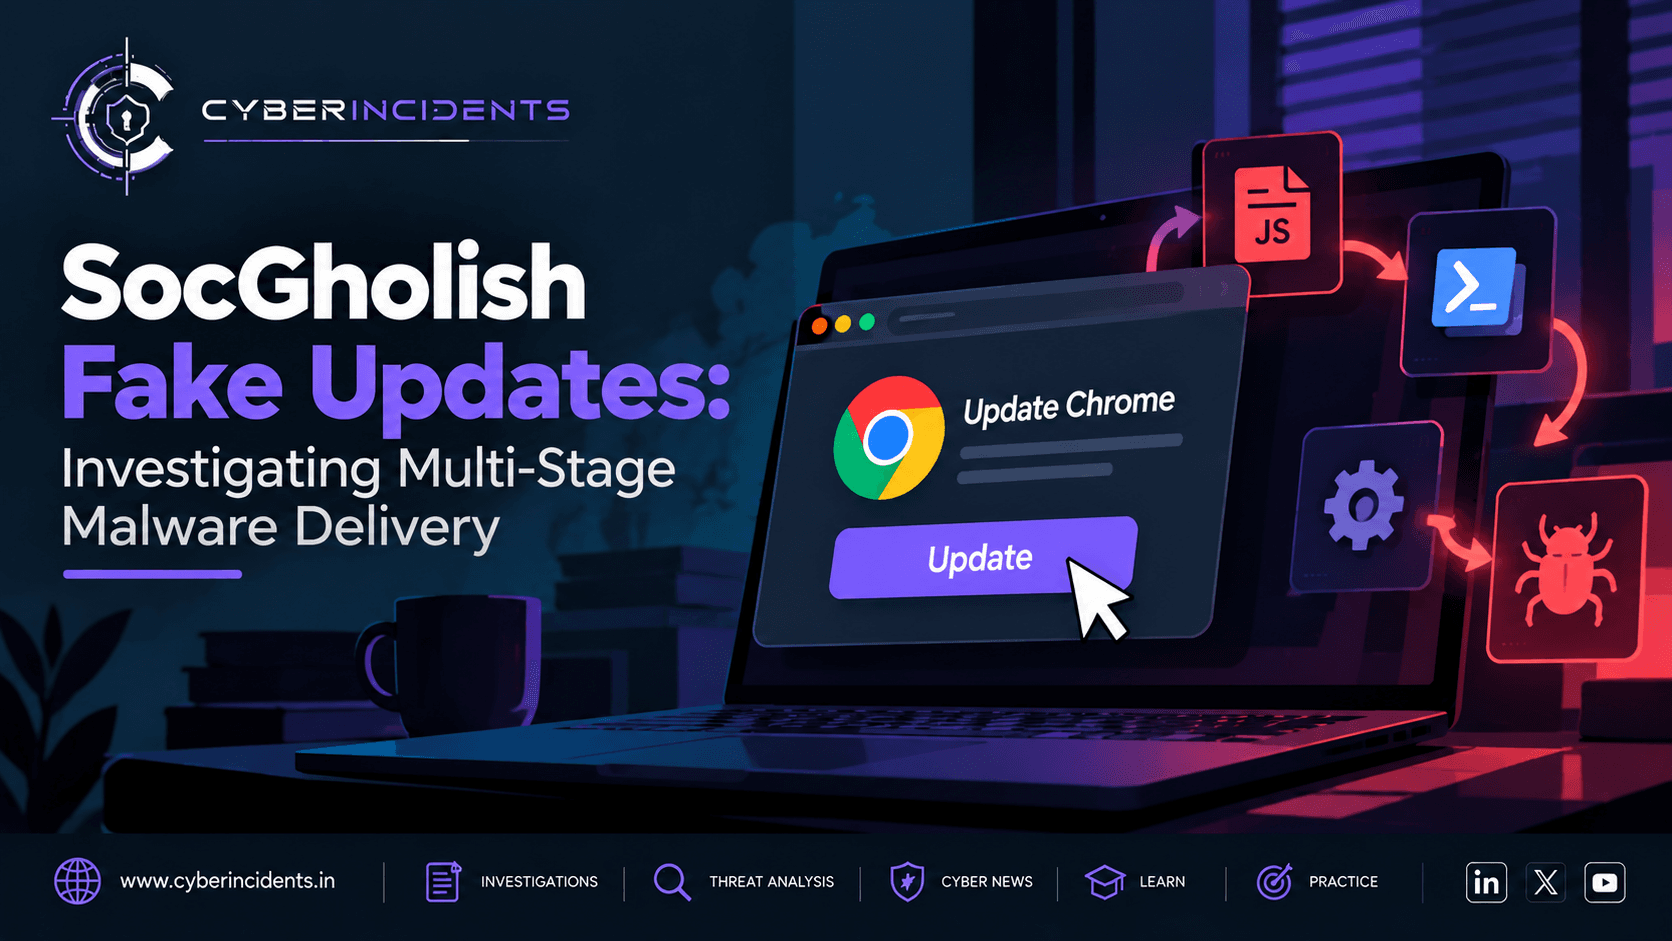
This is the central deception behind SocGholish, a malware delivery operation associated with fake software updates. Attackers compromise legitimate websites or inject malicious scripts into their pages. Selected visitors may then be redirected to fraudulent update pages designed to persuade them to download and execute malicious files.
SocGholish has been active since at least 2017 and is documented by MITRE ATT&CK as a JavaScript-based loader used for initial access. Its operators have used compromised websites to distribute malware and have supplied access that can be used by other cybercriminal operations.
The important distinction is that the website a victim visits may be legitimate, while the content injected into it is malicious. Consequently, an employee does not necessarily need to visit an obviously suspicious domain to encounter this attack.
For SOC analysts, the investigation must answer three questions:
How did the user encounter the fake update?
What executed on the endpoint after the download?
Did the initial loader lead to additional malware or broader compromise?
2. What Is SocGholish?
SocGholish is a JavaScript-based malware loader commonly associated with the name FakeUpdates. It is designed to gain an initial foothold and facilitate the delivery of additional malicious components.
Its delivery model takes advantage of trust in websites and software-update notifications.
Rather than relying exclusively on conventional phishing emails, operators can use compromised websites to expose visitors to malicious content. Injected JavaScript and traffic-distribution mechanisms may determine whether a visitor receives a fake update, depending on factors such as the browser, location, or other eligibility checks.
The resulting attack can involve multiple stages:
A user visits a compromised website.
Injected content presents a fake software-update prompt.
The user downloads and executes the disguised payload.
SocGholish runs and may collect information about the system.
The loader communicates with attacker-controlled infrastructure.
Additional tools or malware may be delivered.
The attacker may pursue remote access, credential theft, lateral movement, or ransomware deployment.
Not every infection follows the same sequence. Payloads and follow-on activity can vary according to the campaign, victim environment, and operator objectives.
3. Stage One: Compromised Websites and Malicious JavaScript
The infection chain may begin before the victim downloads anything.
Attackers compromise a website and introduce malicious JavaScript or other web content. That content can direct selected visitors through additional infrastructure before displaying a fake update prompt.
Traffic-distribution systems may help operators filter visitors and decide which requests should receive malicious content. This can make the activity inconsistent: one user may see a normal page, while another encounters a fake update.
The website owner may also be unaware that their site has been compromised.
What should investigators look for?
When an employee reports a suspicious update prompt, investigators should establish:
The website the user intended to visit.
The complete redirect chain, if available.
The time the prompt appeared.
Whether a file was downloaded.
The download URL, filename, and file hash.
Whether other users visited the same page around the same time.
Browser history, secure web gateway logs, DNS telemetry, proxy records, and endpoint download events may help reconstruct this stage.
A domain should not be classified as malicious solely because it appeared in the browser history. Investigators should distinguish the legitimate website, any compromised page, and the separate infrastructure involved in redirecting visitors or delivering malware.
4. Stage Two: The Fake Update and Initial Execution
The fake update is the social-engineering component of the attack. Its purpose is to persuade the victim to perform an action that allows the malicious payload to execute.
Depending on the campaign, the downloaded item may be a JavaScript file, a ZIP archive containing a script, or another file type. Researchers have documented both ZIP-based delivery and direct delivery of JavaScript payloads.
The file may use a name that resembles a legitimate update component. The name itself is not reliable evidence of authenticity.
Once the user executes the payload, the investigation shifts from browser activity to host-level execution.
Endpoint evidence
Analysts should examine:
Downloaded files and their hashes.
The process responsible for launching the downloaded content.
Script-interpreter execution, including Windows Script Host activity where applicable.
Parent-child process relationships.
Command-line arguments and process timestamps.
Antivirus or EDR detections associated with the file.
File creation and temporary-file activity around execution.
The objective is to establish a reliable connection between the fake-update interaction and the first suspicious execution event.
A downloaded file alone does not prove that it executed. Similarly, a suspicious script process does not independently establish that SocGholish was responsible. Both findings need to be correlated with the rest of the evidence.
5. Stage Three: System Discovery and Environment Profiling
After execution, SocGholish may collect information about the affected system. This helps the operators understand the environment and may influence subsequent activity.
Documented capabilities include identifying the system's username, computer name, domain-related information, operating-system details, and running processes. The malware has also been observed identifying the victim's browser and using location-related information in its delivery logic.
From an investigation perspective, this stage can reveal whether the malware progressed beyond initial execution.
Relevant investigative evidence
EvidenceWhat the analyst should establishProcess executionWhich processes ran after the downloaded file was opened?Account contextUnder which user account did the suspicious activity occur?Domain informationWas the endpoint joined to a corporate Active Directory environment?Process discoveryWas there evidence of enumeration of running processes?Temporary filesWere files created that may contain command output or staged information?EDR telemetryDid the endpoint show suspicious scripting, process access, or follow-on execution?
The presence of discovery activity is important, but it does not automatically mean that credentials were stolen or that lateral movement occurred.
Analysts must identify the actual behaviour observed on the endpoint and avoid inferring actions that the evidence does not support.
6. Stage Four: Command-and-Control and Secondary Payload Delivery
SocGholish is a loader, so its significance extends beyond the initial script execution.
After establishing communication with attacker-controlled infrastructure, it may retrieve additional malicious components. The next stage can vary: an intrusion may involve remote-access tools, information stealers, command-and-control frameworks, or other malware.
Security researchers have documented SocGholish infections associated with tools such as Cobalt Strike, NetSupport, and AsyncRAT, as well as incidents that progressed towards ransomware. These are possible outcomes, not guaranteed components of every infection.
How to investigate the network stage
Review network telemetry around the initial execution timestamp.
Look for:
DNS queries made by the affected host.
Outbound connections shortly after script execution.
Connections to unfamiliar domains or cloud-hosted infrastructure.
Downloads that follow the initial payload.
Repeated communication patterns consistent with command-and-control activity.
Differences between the endpoint's normal network behaviour and the observed connections.
Do not assume that every unfamiliar destination is malicious. Cloud services, content-delivery networks, and shared hosting can serve legitimate and malicious content.
Where possible, correlate network connections with the responsible process and the exact time of execution. A connection made by a suspicious script or newly spawned process is more informative than an isolated DNS query.
7. Stage Five: Follow-On Access and Potential Ransomware Deployment
The initial SocGholish infection may serve as an entry point for additional operators or tools.
If the compromised system is valuable, attackers may attempt to expand access, collect sensitive information, deploy remote-access software, or move towards broader network compromise.
In some incidents, the consequences can include ransomware. However, a SocGholish detection should not automatically be treated as proof that ransomware has been deployed or that the entire network is compromised.
Indicators of possible escalation
Investigators should examine whether the endpoint or related systems show:
New remote-access software or suspicious services.
Unusual authentication activity.
Unexpected administrative processes or privilege changes.
Connections to other internal systems.
Attempts to access security tools or modify protective controls.
Large-scale file modifications or suspicious encryption activity.
Unusual data collection or outbound transfer.
If these behaviours are confirmed, expand the investigation beyond the original host. Review identity logs, endpoint telemetry, server activity, and network traffic to determine whether the incident has spread.
The severity assessment should reflect confirmed impact, not merely the worst-case capability of the malware family.
8. SOC Investigation: A Step-by-Step Workflow
The following workflow can be used when an EDR alert, web-filtering event, or user report suggests a SocGholish fake-update infection.
Step 1: Confirm the initial event
Identify the affected user, endpoint, timestamp, browser, visited website, and downloaded file.
Record the available file hashes and detection details. Preserve browser and network records where possible.
Step 2: Establish whether execution occurred
Review process creation telemetry, script execution events, EDR detections, and parent-child relationships.
Determine whether the user only encountered the fake update or actually executed the downloaded file.
Step 3: Investigate the execution chain
Identify the first suspicious process and its descendants. Review command lines, process paths, signatures, and related file activity.
Look for additional scripts, executables, temporary files, or processes created after the suspected loader ran.
Step 4: Reconstruct network activity
Correlate DNS, proxy, firewall, and endpoint connection records with the execution timeline.
Identify potential payload-download activity and command-and-control communications. Validate destinations using reliable intelligence and the context of the incident.
Step 5: Search for secondary payloads
Inspect endpoint detections and newly created files for evidence of additional malware.
Look for signs of remote-access tools, credential theft, persistence, or ransomware-related activity, but classify each finding separately according to the available evidence.
Step 6: Scope the incident
Search across the environment for related file hashes, domains, process patterns, and other confirmed indicators.
Check whether other users accessed the same compromised website and whether similar execution occurred on their endpoints.
Step 7: Contain and recover
If the investigation supports a malicious infection, follow the incident-response playbook. Actions may include isolating the endpoint, blocking confirmed malicious infrastructure, removing malicious files, revoking affected sessions, and resetting credentials where exposure is suspected.
If secondary access or persistence is identified, removal of the initial script alone is not sufficient. Validate the full scope of the compromise before returning the endpoint to service.
Step 8: Document the conclusion
Record the timeline, evidence, scope, containment actions, and confidence level.
Clearly distinguish between confirmed SocGholish activity, suspected follow-on malware, and potential impacts that were investigated but not observed.
9. Evidence and Indicators of Compromise
The following artefacts can support a SocGholish investigation. They are investigative leads, not a list of universal indicators.
Indicator categoryExamples of evidenceInvestigative purposeWeb activityCompromised pages, redirects, fake-update contentReconstructs initial deliveryDownload artefactsScript files, ZIP archives, file hashesIdentifies the downloaded payloadProcess telemetryScript interpreters, parent-child process chainsEstablishes executionHost discoveryUsername, hostname, domain or process enumerationIdentifies post-execution activityNetwork activityDNS queries, outbound connections, payload downloadsReconstructs external communicationSecondary malwareAdditional executables, remote-access tools, EDR alertsDetermines the scope and severityPersistence artefactsUnexpected services, scheduled tasks, startup changesEstablishes whether access may survive a restart
Do not publish a generic hash, domain, or IP address as a SocGholish IOC unless it has been verified against a reliable source or directly recovered from the analysed sample.
Indicators are campaign-dependent and can change quickly. A valid indicator from an older campaign may no longer be useful for identifying current activity.
10. MITRE ATT&CK Mapping
The following techniques are relevant to documented SocGholish behaviour. Their inclusion in an investigation report should depend on the evidence collected.
TechniqueATT&CK IDRelevanceDrive-by CompromiseT1189Malicious content delivered through a compromised websiteUser Execution: Malicious FileT1204.002Relevant when a user executes a downloaded malicious fileCommand and Scripting Interpreter: JavaScriptT1059.007Execution of the JavaScript-based loaderIngress Tool TransferT1105Downloading additional tools or payloadsSystem Information DiscoveryT1082Collecting operating-system or host informationProcess DiscoveryT1057Enumerating running processesSystem Owner/User DiscoveryT1033Identifying the current userSoftware DiscoveryT1518Identifying software or browser information
MITRE ATT&CK documents SocGholish as software S1124 and describes several of these behaviours.
A mapping should not be added solely because the malware family is known to support a technique. Confirm the relevant activity in the incident wherever telemetry allows.
11. Detection and Prevention Strategies
Web and DNS security
Use web filtering, DNS security, and threat-intelligence enrichment to identify suspicious redirect chains and known malicious infrastructure. Monitor compromised-site activity without assuming that every site involved is intentionally malicious.
Endpoint detection
Prioritise detections for suspicious script execution, unusual process relationships, unexpected payload downloads, and subsequent command execution.
Correlate events instead of relying on a single filename or process name.
Restrict unnecessary script execution
Apply appropriate application-control policies and restrict risky execution paths where operationally feasible. Ensure that users do not need unnecessary permissions to install software.
Improve user awareness
Teach employees that websites generally should not require them to download and execute a script to update a browser. Updates should be obtained through the browser's built-in update mechanism or the software vendor's trusted distribution channel.
Prepare for secondary compromise
Detection and response procedures should cover more than the initial loader. Monitor for remote-access tools, suspicious authentication, privilege changes, and ransomware indicators.
Protect and investigate compromised websites
Organisations operating websites should maintain software and plugins, restrict administrative access, monitor unexpected script changes, and investigate signs of web compromise. A compromised legitimate website can become a delivery point for attacks against its visitors.
12. Recent Disruption and the Continuing Defensive Lesson
In June 2026, law-enforcement and private-sector partners announced disruption efforts targeting SocGholish-related infrastructure under Operation Endgame. Proofpoint reported actions involving server disruption and the disinfection of compromised websites.
Such actions can reduce attacker infrastructure and remove malicious content, but a disruption announcement should not be interpreted as proof that every infection has been remediated or that the broader fake-update threat has disappeared.
For defenders, the practical response remains the same: monitor for suspicious web delivery, validate endpoint execution, investigate secondary payloads, and assess whether an initial infection led to broader compromise.
Organisations should continue applying their normal detection and response controls rather than relying solely on blocklists or assumptions about the status of a criminal operation.
Conclusion
SocGholish demonstrates how attackers can turn a familiar online activity into the beginning of a multi-stage malware infection. By injecting malicious content into compromised websites and impersonating legitimate software updates, operators exploit user trust to deliver a JavaScript-based loader.
The initial execution may be only the first step. System discovery, external communications, secondary payload delivery, and further exploitation can follow, depending on the campaign and the victim's environment.
For SOC analysts, effective investigation depends on reconstructing the entire chain: the website visit, the download, the execution event, the network communications, and any subsequent malicious activity. This allows defenders to distinguish a blocked download from a confirmed infection and a single-host incident from a broader compromise.
The key lesson: A fake update is not merely a suspicious download. It may be the first observable step in a much larger intrusion, and the investigation should continue until the scope and impact are understood.